 Loops House
OxWrit: on-chain authorization for AI agent payments

NEAR HACKATHON
Links
Team
1 member- ANOwner
Ange
Overview
OxWrit, On-Chain Authorization for AI Agent Payments
AI agents increasingly control wallets and payment credentials. However, holding a key does not mean an agent is authorized to execute every transaction. Prompt-based guardrails can be bypassed, while monitoring often detects violations only after execution.
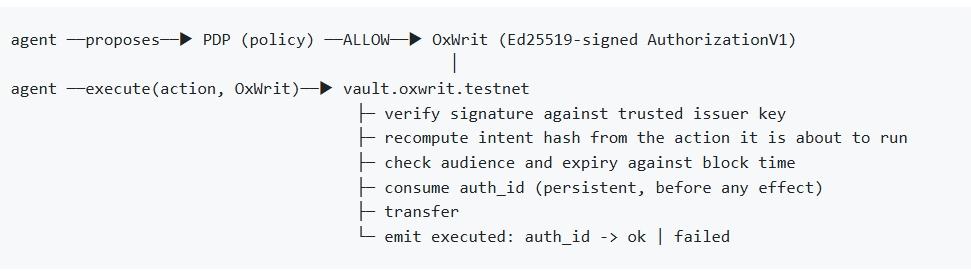
OxWrit introduces an on-chain Policy Enforcement Point (PEP) on NEAR, ensuring that agent-initiated payments execute only when backed by a valid, action-specific authorization.
Before executing a payment, a Policy Decision Point (PDP) evaluates the request and issues an Ed25519-signed OxDeAI AuthorizationV1. The NEAR vault contract independently verifies:
- Issuer authenticity: the authorization signature matches a trusted PDP key.
- Action binding: the intent hash matches the actual vault, recipient, amount, and nonce.
- Context validity: the authorization has the correct audience and has not expired.
- Replay protection: each
auth_idcan be consumed only once.
All checks occur before funds are transferred. Invalid authorizations are rejected without executing the payment.
NEAR provides an additional security boundary through native access-key permissions. The agent uses a FunctionCall key restricted to the vault's execute method, preventing direct transfers or calls to unauthorized contract methods through that key.
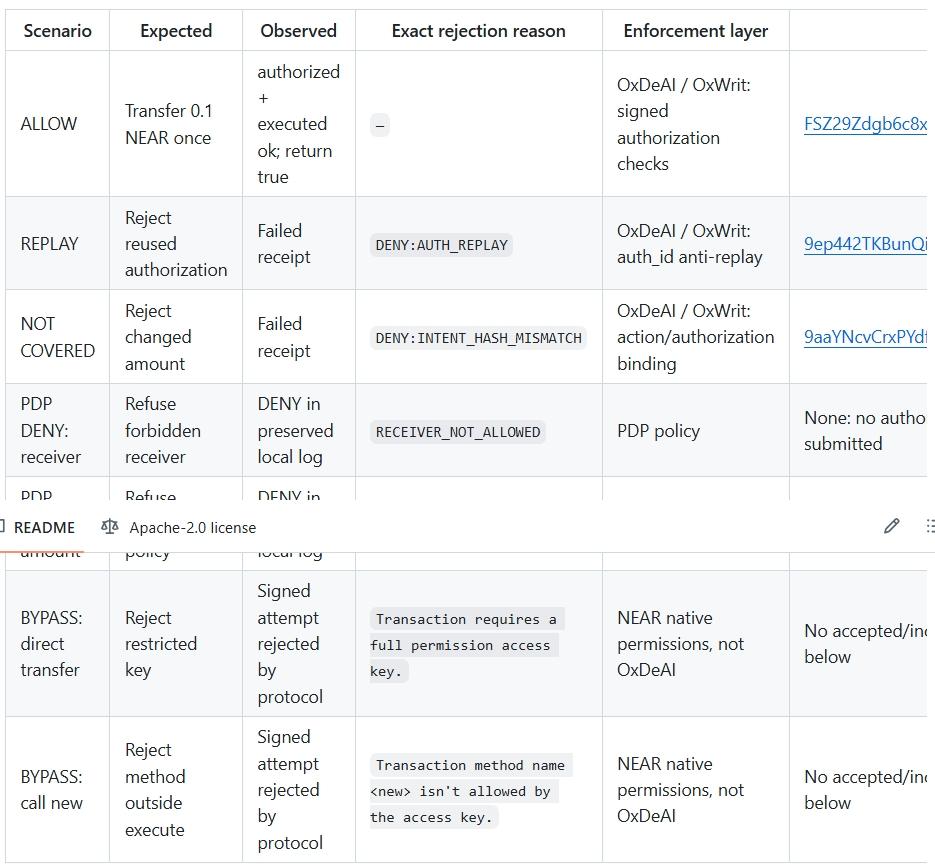
Demonstrated on NEAR Testnet (vault.oxwrit.testnet):
- ALLOW: authorized payment executed successfully.
- REPLAY: reused authorization rejected (
AUTH_REPLAY). - TAMPERING: modified payment amount rejected (
INTENT_HASH_MISMATCH). - POLICY DENIAL: unauthorized recipients and excessive amounts rejected by the PDP.
- BYPASS PREVENTION: direct transfers and unauthorized method calls rejected under the agent's restricted access key.
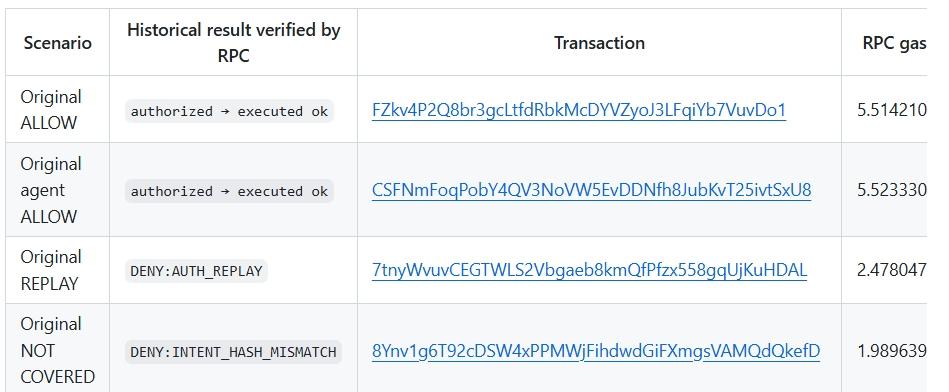
The deployed contract is reproducible from commit 64337b5. A public, read-only verification script (./evidence/verify-onchain.sh) checks deployment properties and historical on-chain evidence without requiring private keys. Its reported results are 16 PASS, 0 FAIL, and 4 NOT_TESTED, with local-only scenarios documented separately.
Built during the hackathon: the Rust authorization verifier, NEAR vault contract, PDP integration, and verification tooling. The underlying OxDeAI protocol and @oxdeai/core existed before the hackathon.
Security scope: OxWrit is an unaudited testnet prototype. The vault's remaining FullAccess key and compromise of the trusted PDP signing key are outside its demonstrated security boundary.
GitHub: https://github.com/AngeYobo/oxwrit
Demo: https://www.loom.com/share/12ddb607a8e544ecb88ddbfef7131a49
OxWrit, Authorize the action, not just the agent.